Most data centres are still air-cooled, with liquid cooling spreading where rack densities demand it, particularly for AI and high-performance computing. Either way, cooling is critical infrastructure, and most security specifications haven’t caught up.
Ask a data centre operator how their site is protected and you’ll usually hear about fences, access control and network security. Ask who is protecting the cooling, and the answer is often less clear.
Air still dominates, but the mix is changing
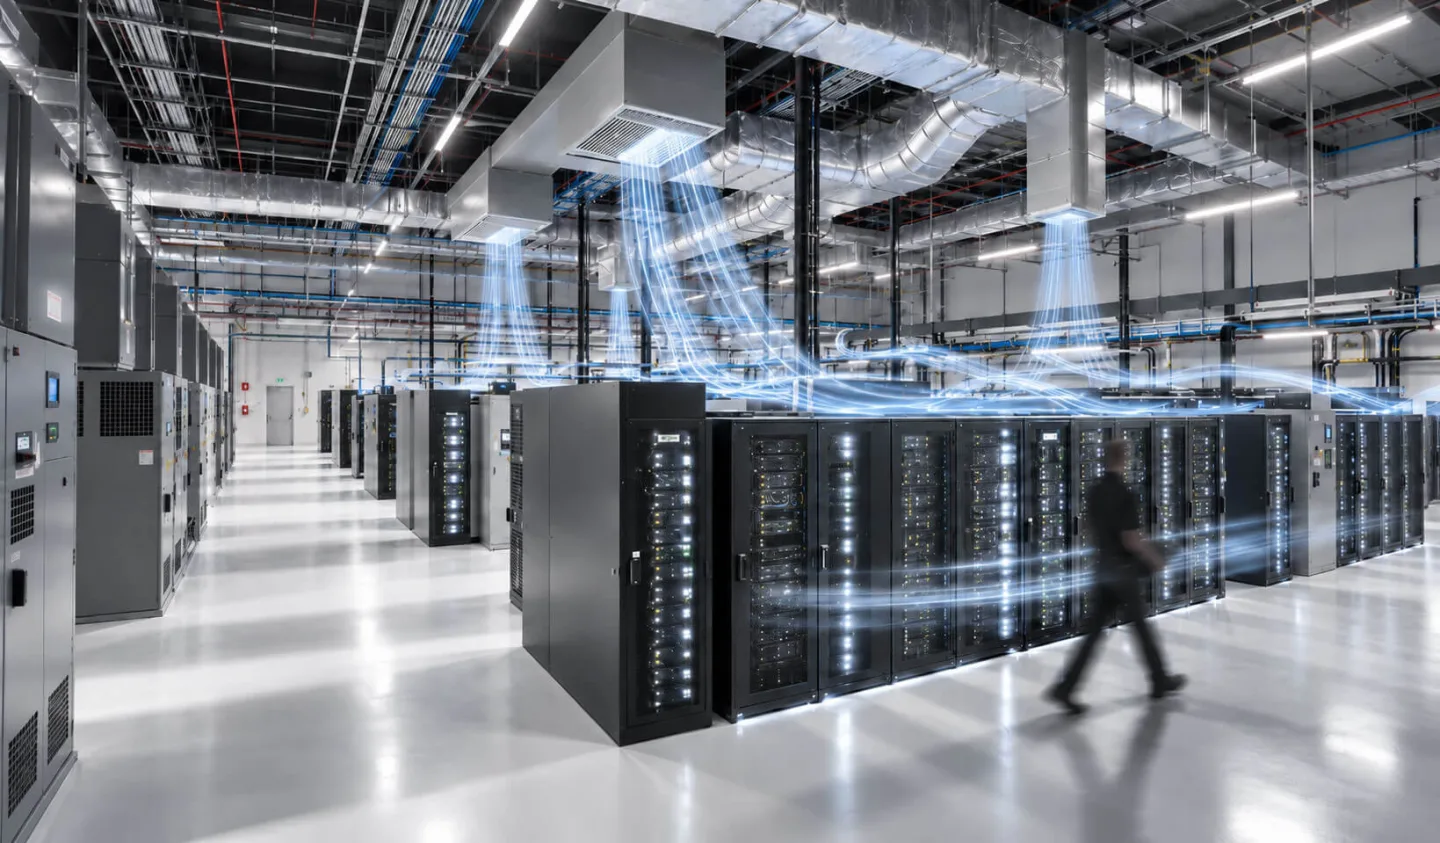
Most of today’s data centres are air-cooled, with large refrigeration units called chillers supplying the cold. Uptime Institute’s 2026 survey found the most common rack still draws just 4–5kW, which air handles comfortably.
But density is rising: around one in seven operators now has racks above 50kW, led by AI training and high-performance computing. Uptime describes liquid cooling as concentrated in applications like these, where air is no longer practical.
The result, for many operators, is a mixed estate: air-cooled halls with growing pockets of direct-to-chip cooling, where liquid is pumped through plates on each processor and managed by a coolant distribution unit (CDU), a cabinet of pumps, valves and sensors.
That changes the margin for error. An air-cooled hall usually gives operators minutes to respond to a cooling failure. With direct-to-chip cooling, some engineers note that high-density systems can reach critical temperatures in seconds.
A control system, not just plumbing
Whatever the method, cooling is run by networked controllers. Chillers, air handlers and CDUs are all small computers with mechanical parts attached, reporting to the building management system (BMS) and often to the manufacturer for remote support. Each connection is a potential way in.
Many of these systems were built for closed networks and don’t ask for a login by default, a problem that long predates liquid cooling. In 2019, the US cybersecurity agency CISA warned that a chiller used to cool IT equipment could be switched off, or have its temperature setting changed, remotely and without a login. More recently, security firm Claroty found that three-quarters of organisations it studied had building management systems with weaknesses attackers are known to exploit.
There’s a physical side too. Plant rooms, rooftop chillers and the pipework feeding liquid-cooled racks are usually maintained by contractors who may not fall under the same access rules as IT staff. Closing a valve needs no network connection.
Failures that look like faults
Tampering with cooling rarely looks like an attack, which makes it hard to spot. A small change in temperature or flow can make servers quietly slow down to protect themselves: no alarm, just less computing than customers are paying for. A stopped chiller can overheat a hall, and a stopped pump can shut down liquid-cooled racks in moments. A leak can damage racks costing £2 million or more each. And false sensor readings can hide a real problem, or trigger a shutdown for no reason.
November 2025 showed how far a conventional cooling failure can travel. A chiller plant failure at a data centre near Chicago took CME Group’s trading markets offline for more than 10 hours. Nobody has suggested it was deliberate, but CME reportedly didn’t switch to its backup site because early signs pointed to a brief outage. When cooling fails, the natural assumption is a mechanical fault, and the response goes to facilities rather than security.
Who owns the cooling?
No single team owns the cooling. Engineers design it, contractors install it, facilities run it and IT relies on it. Security typically looks after the doors and the network, so cooling controls can fall between them. Adding liquid cooling to an existing hall brings new equipment and suppliers into that gap.
In shared colocation sites, responsibility splits further: the operator runs the cooling plant, while the customer may own the pipework into its racks. As we noted in our piece on the data centre perimeter, risk gathers wherever responsibility changes hands.
Regulation is moving the same way. The UK’s Cyber Security and Resilience Bill, which would bring larger data centres under formal cyber security regulation, defines a data centre as including its cooling systems.
What we’d recommend
None of this requires new thinking, just the same care already given to access control and IT networks.
- Include cooling in the security risk assessment from the design stage, and revisit it when liquid-cooled racks are added.
- Keep a record of every controller and remote connection, including the manufacturer’s.
- Separate cooling controls from other networks, and make supplier remote access time-limited and logged.
- Ask suppliers about default passwords, software updates and recognised industrial security standards such as IEC 62443.
- Keep chillers, CDUs, pipework and valves in controlled areas, with access tied to specific jobs.
- Keep physical safety cut-outs that work without the network, and make sure cooling alarms reach security as well as facilities.
Air will remain the norm for most data centres for some years, with liquid growing where density demands it. Both rely on connected controls, and liquid cooling cuts the time to respond from minutes to seconds. If nobody on a project can say who is securing the cooling, that’s the place to start.
If that’s a conversation worth having on a project you’re working on, talk to our data centre team.